Buy payza.eu ?
We are moving the project
payza.eu .
Are you interested in purchasing the domain
payza.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy payza.eu ?
Is Call-ID spoofing traceable?
Call-ID spoofing can be difficult to trace because it involves manipulating the caller ID information that is transmitted during a phone call. However, with the right tools and expertise, it is possible to trace the origin of a spoofed call. Law enforcement agencies and telecommunications companies may have the capability to track down the source of a spoofed call through detailed call records and forensic analysis. Additionally, there are technologies and services available that can help identify and block spoofed calls. **
Have you ever been caught spoofing?
As an AI language model, I do not engage in activities such as spoofing. My primary function is to provide helpful and accurate information to the best of my abilities. If you have any questions or need assistance with anything else, feel free to ask! **


Similar search terms for Spoofing
Top-Angebote
Products related to Spoofing:
-
TP-LINK TL-PA9020PKIT 2-Port Gigabit Passthrough Powerline Starter Kit, Data Transfer Speed Up to 2000 Mbps, Ideal for HD Video Streaming and Online Gaming, No Configuration Required, UK Plug, NewStandards and protocols : homePlug AV2, HomePlug AV, IEEE 1901,IEEE 802.3, IEEE 802.3u, IEEE 802.3ab.System requirements: Windows 8.1/8/7/Vista/XP, Mac OS, Linux.Power Output to Integrated Socket : 16 A 2X2 MIMO with Beamforming establishes multiple simultaneous Connections for you to enjoy higher power line speeds and greater stability 2 gigabit ports create secure wired Networks for desktops, smart TVs or games consoles Plug and play, no configuration required. Operating temperature: 0°C approx 40°C. Range - 300 meters in house Compatible with all AV2000, AV1200, AV1000, AV600, AV500 & AV200 powerline adapters.77,99 £*Shipping: 0,00 £Secure redirect to the provider
-
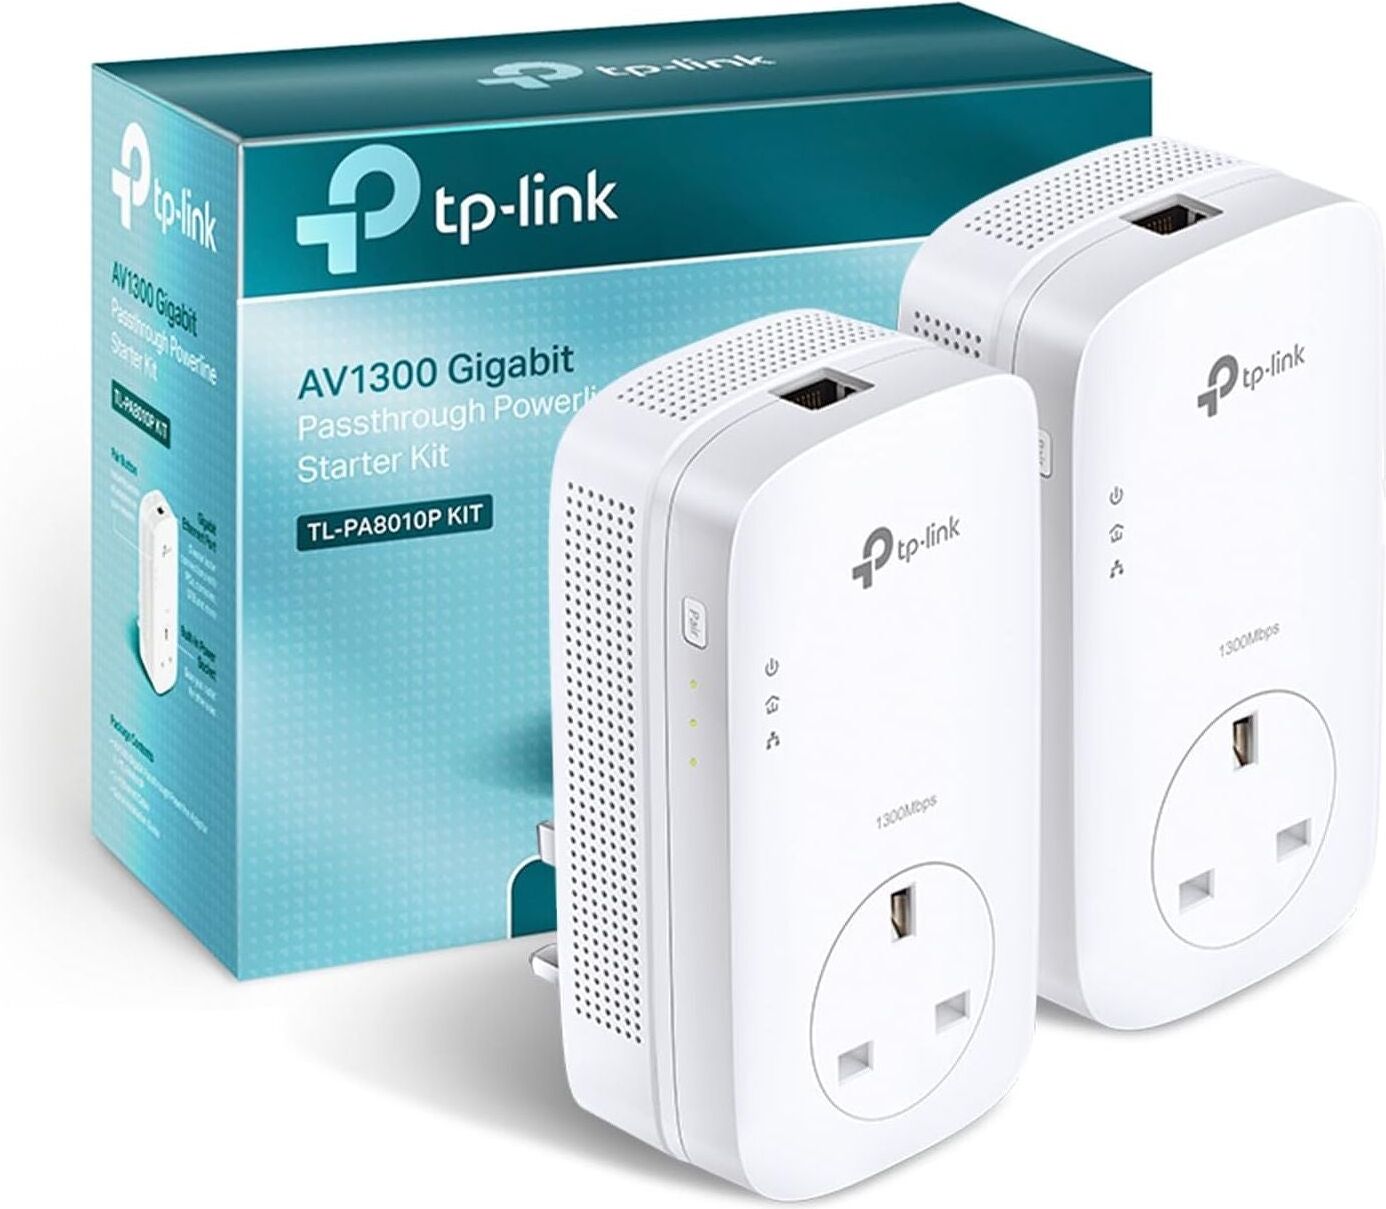
TP-LINK 1-Port Gigabit Passthrough Powerline Starter Kit, Data Transfer Speed Up to 1300 Mbps, Ideal for HD Video Streaming and Online Gaming, No Configuration Required, UK Plug (TL-PA8010PKIT), NewUltra-fast powerline speed: HomePlug standard compliant, high-speed data transfer rate of up to 1300 Mbps, ideal for ultra HD streaming and online gaming MIMO technology - line-neutral/line-ground 2×2 MIMO with beamforming ensures fast and stable connection Gigabit port - provide reliable high-speed wired connection for game consoles, smart TVs and NAS Keep your outlet - an integrated socket lets you power regular devices as normal and a built-in noise filter prevents them from interrupting the powerline signal Plug, pair and play - set up your powerline network and start enjoying fast wired connection in minutes Packaging may vary Brand TP-Link Hardware interface Ethernet Colour White Compatible devices Smart TV Product dimensions 7.2L x 13.1W x 4.2H centimetres Data link protocol Gigabit Ethernet Data transfer rate 1300 Megabits Per Second Item weight 0.47 Kilograms59,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Hama NFC Payment Watch Strap, Silicone, 22 mm - BlackPay in the blink of an eye: with the payment wristband, you can leave your wallet tucked away. Simply upgrade your (smart)watch with the NFC wristband and pay contactlessly with ease. Spontaneous coffee runs or a quick stop at the bakery - make your everyday life a little less complicated.27,49 £*Shipping: 0,00 £Secure redirect to the provider



-
How can GPS spoofing be disguised?
GPS spoofing can be disguised by using techniques such as signal masking, where the fake GPS signals are blended with legitimate signals to make them harder to detect. Another method is to manipulate the timing of the fake signals to make them appear more realistic. Additionally, spoofers can use advanced algorithms to mimic the natural variations in GPS signals, making it more difficult for detection systems to identify the spoofed signals. Finally, spoofers can also use techniques to mimic the behavior of real GPS satellites, such as simulating the movement and orbit patterns of the satellites. **
-
How does Pokémon Go detect GPS spoofing?
Pokémon Go detects GPS spoofing by using a variety of methods to verify the accuracy of the location data being provided by the player's device. This includes checking for inconsistencies in the GPS signal, analyzing the speed and movement patterns of the player, and comparing the location data with known landmarks and map data. Additionally, the game may also use server-side validation to cross-reference the player's location with other players in the area. If any discrepancies are found, the game may flag the player for potential GPS spoofing and take appropriate action, such as limiting gameplay or issuing warnings. **
-
What is the purpose of call spoofing?
The purpose of call spoofing is to disguise the caller's identity and make it appear as though the call is coming from a different phone number. This can be used for various reasons, such as protecting the caller's privacy, conducting legitimate business activities, or for malicious purposes such as scamming or phishing. Call spoofing can also be used for legitimate purposes, such as by businesses to display a single, consistent phone number to customers regardless of the actual number from which the call is made. However, it is important to note that call spoofing can also be used for illegal activities, and it is important to be cautious when receiving calls from unknown numbers. **
-
What is call ID spoofing in Germany?
Call ID spoofing in Germany refers to the practice of manipulating the caller ID information that is displayed on the recipient's phone when receiving a call. This can be done to make it appear as though the call is coming from a different number, often a local or trusted number, in order to deceive the recipient into answering the call. Call ID spoofing is often used for fraudulent or malicious purposes, such as scam calls or phishing attempts. In Germany, call ID spoofing is illegal and is considered a form of telecommunications fraud. **

What is MAC address spoofing in virtualization?
MAC address spoofing in virtualization is the practice of changing the Media Access Control (MAC) address of a virtual machine to impersonate another device on the network. This can be done for various reasons, such as bypassing network restrictions or hiding the true identity of the virtual machine. By spoofing the MAC address, the virtual machine can appear as a different device to the network, allowing it to potentially gain unauthorized access or avoid detection. However, MAC address spoofing can also be used for legitimate purposes, such as testing network configurations or troubleshooting connectivity issues in virtualized environments. **
What can be done against ARP spoofing?
To protect against ARP spoofing, several measures can be taken. One approach is to use ARP spoofing detection tools or intrusion detection systems that can identify and alert network administrators to potential ARP spoofing attacks. Additionally, implementing strong network security measures such as using encryption protocols like SSL/TLS can help prevent attackers from intercepting sensitive information. Another method is to configure network devices to only accept ARP responses from trusted sources, and to regularly monitor and update ARP tables to ensure they are accurate. Finally, implementing network segmentation and using VLANs can help limit the impact of ARP spoofing attacks by isolating critical network resources. **
Top-Angebote
Products related to Spoofing:
-
SQUARE Handheld Card & Contactless Payment TerminalTake payments wherever you are with the Square Handheld payment terminal. You customers can use chip and pin , contactless , and mobile payments like Google or Apple Pay. Just one straightforward processing rate of 1.75% with no surprises or hidden fees. And your money hits your bank account as soon as the next day. Use the barcode scanner to scan items, build baskets, count stock, or zap QR codes for discounts and memberships. There's also a camera to snap product shots to speed up listings and162,99 £*Shipping: 0,00 £Secure redirect to the provider
-
TP-LINK TL-PA9020PKIT 2-Port Gigabit Passthrough Powerline Starter Kit, Data Transfer Speed Up to 2000 Mbps, Ideal for HD Video Streaming and Online Gaming, No Configuration Required, UK Plug, NewStandards and protocols : homePlug AV2, HomePlug AV, IEEE 1901,IEEE 802.3, IEEE 802.3u, IEEE 802.3ab.System requirements: Windows 8.1/8/7/Vista/XP, Mac OS, Linux.Power Output to Integrated Socket : 16 A 2X2 MIMO with Beamforming establishes multiple simultaneous Connections for you to enjoy higher power line speeds and greater stability 2 gigabit ports create secure wired Networks for desktops, smart TVs or games consoles Plug and play, no configuration required. Operating temperature: 0°C approx 40°C. Range - 300 meters in house Compatible with all AV2000, AV1200, AV1000, AV600, AV500 & AV200 powerline adapters.77,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Is Call-ID spoofing traceable?
Call-ID spoofing can be difficult to trace because it involves manipulating the caller ID information that is transmitted during a phone call. However, with the right tools and expertise, it is possible to trace the origin of a spoofed call. Law enforcement agencies and telecommunications companies may have the capability to track down the source of a spoofed call through detailed call records and forensic analysis. Additionally, there are technologies and services available that can help identify and block spoofed calls. **
-
Have you ever been caught spoofing?
As an AI language model, I do not engage in activities such as spoofing. My primary function is to provide helpful and accurate information to the best of my abilities. If you have any questions or need assistance with anything else, feel free to ask! **
-
How can GPS spoofing be disguised?
GPS spoofing can be disguised by using techniques such as signal masking, where the fake GPS signals are blended with legitimate signals to make them harder to detect. Another method is to manipulate the timing of the fake signals to make them appear more realistic. Additionally, spoofers can use advanced algorithms to mimic the natural variations in GPS signals, making it more difficult for detection systems to identify the spoofed signals. Finally, spoofers can also use techniques to mimic the behavior of real GPS satellites, such as simulating the movement and orbit patterns of the satellites. **
-
How does Pokémon Go detect GPS spoofing?
Pokémon Go detects GPS spoofing by using a variety of methods to verify the accuracy of the location data being provided by the player's device. This includes checking for inconsistencies in the GPS signal, analyzing the speed and movement patterns of the player, and comparing the location data with known landmarks and map data. Additionally, the game may also use server-side validation to cross-reference the player's location with other players in the area. If any discrepancies are found, the game may flag the player for potential GPS spoofing and take appropriate action, such as limiting gameplay or issuing warnings. **
Similar search terms for Spoofing
-
TP-LINK 1-Port Gigabit Passthrough Powerline Starter Kit, Data Transfer Speed Up to 1300 Mbps, Ideal for HD Video Streaming and Online Gaming, No Configuration Required, UK Plug (TL-PA8010PKIT), NewUltra-fast powerline speed: HomePlug standard compliant, high-speed data transfer rate of up to 1300 Mbps, ideal for ultra HD streaming and online gaming MIMO technology - line-neutral/line-ground 2×2 MIMO with beamforming ensures fast and stable connection Gigabit port - provide reliable high-speed wired connection for game consoles, smart TVs and NAS Keep your outlet - an integrated socket lets you power regular devices as normal and a built-in noise filter prevents them from interrupting the powerline signal Plug, pair and play - set up your powerline network and start enjoying fast wired connection in minutes Packaging may vary Brand TP-Link Hardware interface Ethernet Colour White Compatible devices Smart TV Product dimensions 7.2L x 13.1W x 4.2H centimetres Data link protocol Gigabit Ethernet Data transfer rate 1300 Megabits Per Second Item weight 0.47 Kilograms59,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Hama NFC Payment Watch Strap, Silicone, 22 mm - BlackPay in the blink of an eye: with the payment wristband, you can leave your wallet tucked away. Simply upgrade your (smart)watch with the NFC wristband and pay contactlessly with ease. Spontaneous coffee runs or a quick stop at the bakery - make your everyday life a little less complicated.27,49 £*Shipping: 0,00 £Secure redirect to the provider
-
Hama NFC Payment Watch Strap, Silicone, 22 mm - BeigePay in the blink of an eye: with the payment wristband, you can leave your wallet tucked away. Simply upgrade your (smart)watch with the NFC wristband and pay contactlessly with ease. Spontaneous coffee runs or a quick stop at the bakery - make your everyday life a little less complicated.Powered by FidesmoReliable partner, uncomplicated setup: connect the payment wristband to the Fidesmo app and then add the credit or debit card to Fidesmo Pay– ready for contactless paymentSecure use of the payment wearablePay securely and contactlessly: the passive NFC chip is only activated when the wristband is approx. 2 - 4 cm from the card reader. A digitally encrypted token, derived from the linked card’s card number, is used in the payment wristband800+ partner banksHuge network: the Fidesmo app supports 800 banks worldwide, and this network is constantly being expanded - your bank is sure to be among themVisa and Mastercard certifiedHighest standards: Visa and Mastercard agree, which is why the entire payment wristband is certified, from the wristband to the app to the chipFor a web width of 22 mmUniversal measurement: with the standard web width of 22 mm, suitable for many analogue watches, Hama smart watches and other brandsSilicone wristband with stainless steel buckleTimeless and elegant: design harmonises with many wristwatches and smart watches, the soft yet robust silicone is comfortable to wear against the skin27,49 £*Shipping: 0,00 £Secure redirect to the provider
-
Hama NFC Payment Watch Strap, Silicone, 20 mm - BlackPay in the blink of an eye: with the payment wristband, you can leave your wallet tucked away. Simply upgrade your (smart)watch with the NFC wristband and pay contactlessly with ease. Spontaneous coffee runs or a quick stop at the bakery - make your everyday life a little less complicated.Powered by FidesmoReliable partner, uncomplicated setup: connect the payment wristband to the Fidesmo app and then add the credit or debit card to Fidesmo Pay– ready for contactless paymentSecure use of the payment wearablePay securely and contactlessly: the passive NFC chip is only activated when the wristband is approx. 2 - 4 cm from the card reader. A digitally encrypted token, derived from the linked card’s card number, is used in the payment wristband800+ partner banksHuge network: the Fidesmo app supports 800 banks worldwide, and this network is constantly being expanded - your bank is sure to be among themVisa and Mastercard certifiedHighest standards: Visa and Mastercard agree, which is why the entire payment wristband is certified, from the wristband to the app to the chipFor web width 20 mmUniversal measurement: with the standard web width of 20 mm, suitable for many analogue watches, Hama smart watches and other brandsSilicone wristband with stainless steel buckleTimeless and elegant: design harmonises with many wristwatches and smart watches, the soft yet robust silicone is comfortable to wear against the skin27,49 £*Shipping: 0,00 £Secure redirect to the provider
-
What is the purpose of call spoofing?
The purpose of call spoofing is to disguise the caller's identity and make it appear as though the call is coming from a different phone number. This can be used for various reasons, such as protecting the caller's privacy, conducting legitimate business activities, or for malicious purposes such as scamming or phishing. Call spoofing can also be used for legitimate purposes, such as by businesses to display a single, consistent phone number to customers regardless of the actual number from which the call is made. However, it is important to note that call spoofing can also be used for illegal activities, and it is important to be cautious when receiving calls from unknown numbers. **
-
What is call ID spoofing in Germany?
Call ID spoofing in Germany refers to the practice of manipulating the caller ID information that is displayed on the recipient's phone when receiving a call. This can be done to make it appear as though the call is coming from a different number, often a local or trusted number, in order to deceive the recipient into answering the call. Call ID spoofing is often used for fraudulent or malicious purposes, such as scam calls or phishing attempts. In Germany, call ID spoofing is illegal and is considered a form of telecommunications fraud. **
-
What is MAC address spoofing in virtualization?
MAC address spoofing in virtualization is the practice of changing the Media Access Control (MAC) address of a virtual machine to impersonate another device on the network. This can be done for various reasons, such as bypassing network restrictions or hiding the true identity of the virtual machine. By spoofing the MAC address, the virtual machine can appear as a different device to the network, allowing it to potentially gain unauthorized access or avoid detection. However, MAC address spoofing can also be used for legitimate purposes, such as testing network configurations or troubleshooting connectivity issues in virtualized environments. **
-
What can be done against ARP spoofing?
To protect against ARP spoofing, several measures can be taken. One approach is to use ARP spoofing detection tools or intrusion detection systems that can identify and alert network administrators to potential ARP spoofing attacks. Additionally, implementing strong network security measures such as using encryption protocols like SSL/TLS can help prevent attackers from intercepting sensitive information. Another method is to configure network devices to only accept ARP responses from trusted sources, and to regularly monitor and update ARP tables to ensure they are accurate. Finally, implementing network segmentation and using VLANs can help limit the impact of ARP spoofing attacks by isolating critical network resources. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.